Thursday, October 25, 2012

What is mean by computer forensics

Computer forensics is also known by the name of digital forensics is a branch of forensic science pertaining to legal evidence found in computers and digital storage media.

The goal of computer forensics is to explain the circumstances now are of a digital artifact. The term digital artifact can include a computer system, storage media (such as flash disk, hard disk, or CD-ROM), an electronic document (e.g. an email message or JPEG images), or even a series of packages that are switching in computer networks. The explanation could be simply "there's information here?" to "elaborate as what the sequence of events that led to the current situation?".

Computer forensics is also used to eradicate corruption and fraud (fraud) in cyberspace (internet). The investigation of corruption and fraud carried out by taking electronic data and then analyzed for use in court (admissible) as evidence of the legal data records should not be subjected to the slightest changes of the initial conditions of the data found. If the data is changed then it cannot be used in court (the data are no longer authentic).

The use of computer forensics for example for:

1. looking for evidence of fraud or corruption committed by employees
2. Performs analysis on a compromised computer system hackers. How do the hackers get access and what it does.
3. do the recovery lost data either intentional or not, even after a hard disk format or the use of others.

To be submitted as electronic evidence in court, the results of computer forensics should be:

1. meet certain standards, namely (1) admissible (2) authentic (3) complete (4) believable (5) reliable
2. computer forensics tools must be validated methodology. who know but just doang ngakunya abal-abal
3. the electronic storage media must be clearly marked ' chain of custody ' since the initial capture until finally submitted to the Court
4. in general the electronic storage media examination should be done at the owner's permission (with a letter of approval or ' letter of consent '), unless it is done by the authority of law (in wake of indo Attorney, police, KPK)

In the process of computer forensics, data retrieval is known by the term ' computer forensic imaging ' where the suspect hard drives made copy of it is exactly the same (including also the data that was deleted and the technical areas of the hard drive unreadable in the operating system).

Software used on computer forensics is forensic imaging with the aim is make copies of identical electronic data from the target. Imaging process keeping in order that preliminary data do not experience changes with how to make the ' write blocked'terhadap electronic storage media. The Hardware and software that are used specifically for keeping the data in order to remain intact as before (no change) can even evoke the files that have been erased. It aims to find evidence of perpetrators of corruption and fraud.

Some of the vendors who provide computer forensics technology such as Parabens, Guidance (EnCase), GetData (Mount Image), etc.

Searching Unallocated and Slack Space for Text 

Now let’s go back to the original image. The restored disk (or loopmounted disk image) allowed you to check all the files and directories (logicalview). What about unallocated and slack space (physical view)? We will now

analyze the image itself, since it was a bit for bit copy and includes data in theunallocated areas of the disk.Let’s assume that we have seized this disk from a former employee of alarge corporation. The would­be cracker sent a letter to the corporationthreatening to unleash a virus in their network. The suspect denies sending theletter. This is a simple matter of finding the text from a deleted file (unallocatedspace).

Sunday, October 7, 2012

Buffer Overflow with Fuzzer and Fuzzing use WarFTPD & Ollydbg

Buffer Overflow
Buffer overflow itself is a process that goes on inside a computer memory system in which there is an normal process at the time of the temporary data storage in memory i.e. when there is data that will be stored exceeds the capacity of the buffer (temporary storage) in memory.

FUZZER
fuzzer itself is a word that is widely used in the world of science technology one is fuzzy logic, but this discussion on fuzzer no his relationship with fuzzy logic, Fuzzer is a mention to the applications used on the process of fuzzing.

FUZZING
fuzzing is an early stage which is sure to be done by a security researcher, an application will be in line to manage the data that is not normal, so it will be seen how applications handle data as well as the process of error handling by the application, from the process here, a researcher can see if there's a gap in security application that can be exploited.

Tools
tools that will be used as follows  :
* Ollydbg as a debugger
* Fuzzer
to do the process Fuzzing
* Phyton,
used to create an application fuzzer and exploit

WarFTPD
Applications that will be used as the target is the application of WarFTPD made by Jarle (jgaa) Aase, is an FTP server application running on a Windows operating system.as seen in the image below  :


For the application, to be exploited is an FTP server application, so here I am trying to make a simple fuzzer can send data at FTP protocol. the fuzzer  is created using a language Python.

as the example below  :
#!/usr/bin/python
import socket
s= socket.socket(socket.AF_INET,socket.SOCK_STREAM)
buffer ="\x41" * 1000
s . connect (('192.168.56.101 ' ,21))
data =s.recv (1024)
print("sendingevildatavia USER command...")
s.send('USER '+buffer+'\r \n')
data = s.recv (1024)
s.send('PASS PASSWORD'+'\r \n')
s.close()
print ("Finish")

To run WarFTP server, select the Start menu Properties-> Service
the status of WarFTP will become idle.To check whether the server is running and can be contacted via the BackTrack system, try to connect to FTP using NC, run the following command :


the next process is to try to run an application fuzzer which adauntuk runs when the command line, make sure that the window's previous Virtualbox can be seen clearly, the goal is to see what happens to the application server WarFTP.root@bt:~#python BackTrack.py


This time will also be used as an application for Ollydbg perform debugging on an application server WarFTP


for Ollydbg can see what happens when the application crashes, run WarFTP server through applications, when Ollydbg WarFTP server application tried to run back, then an Error message will appear.
to prevent the occurrence of such error appeared again during the process of development, please follow these steps :

*
delete the file FtpDaemon.
* run WarFTP server application again.
* create a user through the User Security dummies.


run WarFTP back when walking normally without the memuculkan error messages, run WarFTP server applications through the Ollydbg.


then it would appear like the following :


lets go , now through the application Konsole on BackTrack, go into the folder, such as the following :
#cd /opt/metasploit/msf3/tools/

If it looks pattern_create.rb
run to generate as much as 1000 byte data, run like this :
./pattern_create.rb 1000 > string_pattern.txt


look the strings as much as 1000 characters, starting from the character "Aa0Aa1Aa2Aa3A" until the character "Bh0Bh1Bh2B"
After the string pattern has been successfully created, the next step enter this data into an application fuzzer which has previously been made, the data pattern that is going to replace the character "A" data on a fuzzer, use a text editor to modify existing scripts in an application fuzzer.


After changing into a collection of pattern strings generate results from pattern_create. rb, continue the next step, run WarFTP server applications through the Ollydbg.


Unlike before, the current value from the register in the memory the application server is fully WarFTP with string pattern that had been incorporated into an application fuzzer, note the data contained in the register.Now use the pettern_offset application will calculate how many bytes of data from the initial pattern to stirng contained in such registers
do konsole as below :
#./pattern_offset.rb 32714131-> Nilai EIP
 486 -> EIP
It takes data of 485 bytes
#./pattern_offset.rb q4Aq5Aq-> Nilai ESP
493
-> to achieve the required data stack of 493 bytes


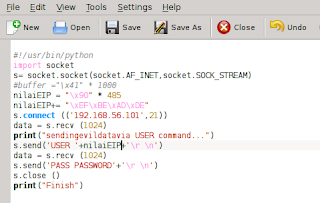
now continue by entering such a fuzzer script below, and proceed with as the previous step..


now consider the value that appears in the window stack and registers in Ollydbg, seen that the value in register EIP be DEADBEEF.


run the application using the Ollydbg, on a Special Executable modules,
then it would appear like the following.


If it looks like the above, proceed to determine which libraries you want to use, double click on the file name, then it will appear as follows.
It appears as below, now do right click in the main window: Search For-> Command.


the input  JMP ESP in window and press the find Command Find


then it will look 7E429353 address JMP ESP, it's on me,
such as the following:


the next thing to do is change the offset address into little endian format, from 7E429353 to \x53\x93\x42\x7E, note the following script:


now run WarFTP Ollydbg and again as before,
then it will appear as follows:


now run WarFTP Ollydbg and again as before,
right-click the selected Breakpoint-> memory, on access.
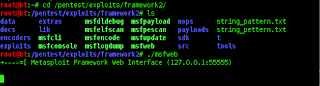
next run on the console, run the ./msfweb.


Now we will go on the payload, payload that will choose in the next build, Metasploit will display the configuration menu of the payload type of the shell as it looks like the following figure,don't forget after you finish press generate to generate the payload has been selected.:


now live the payload that is insert the code into the application that has been used previously, such as the following:


now run WarFTP Ollydbg and again as before, if not in error then run with # telnet 192.168.56.101 4444, then it will occur as follows :


Install Mutillidae Backtrack 5


 Well, now we are trying to install the Mutillidae.
Well ... If you don't already have a download on the internet, mutillidae
or download the link below ...:
http://sourceforge.net/projects/mutillidae/files/latest/download

What if you already download now lives we Exstrac to the root

like below ...:


When it's on Exstrac now living in the run to the Terminal.......:

Install aphace2 first if not installed.After that continue with Terminan..:


After that install live MYSQL server:


Saturday, October 6, 2012

STACK BUFFER OVERFLOW EASY RM TO MP3 CONVERTER

Buffer Overflow
Buffer overflow itself is a process that goes on inside a computer memory system in which there is an normal process at the time of the temporary data storage in memory i.e. when there is data that will be stored exceeds the capacity of the buffer (temporary storage) in memory.

FUZZER
fuzzer itself is a word that is widely used in the world of science technology one is fuzzy logic, but this discussion on fuzzer no his relationship with fuzzy logic, Fuzzer is a mention to the applications used on the process of fuzzing.

FUZZING
fuzzing is an early stage which is sure to be done by a security researcher, an application will be in line to manage the data that is not normal, so it will be seen how applications handle data as well as the process of error handling by the application, from the process here, a researcher can see if there's a gap in security application that can be exploited.

Tools
tools that will be used as follows  :
* Ollydbg as a debugger
* Fuzzer
to do the process Fuzzing
* Phyton,
used to create an application fuzzer and exploit


Before we start you need to have the application of EASY RM TO MP3 CONVERTER,
like the following :


For the application EASY RM TO MP3 CONVERTER, so here I am trying to make a simple fuzzer can send data at Mp3 protocol. the fuzzer  is created using a language Python.

as the example below  :

Now we run does occur on the application crash Easy RM MP3 converter,
in the event of a crash it will arise as follows :


 now start to use Ollydbg,so we know the crash it on the EIP does not,

Open Ollydbg and Easy RM MP3 converter, the Ollydbg click file-> tattach->select RM2MP3Converter->attach->and then Turn on and then run RM2MP3, click load->the input file name and files of type->Open to clarify do as follows :


ow start to figure out how many bytes, then using pattern_create, run the command as follows:
./pattern_create.rb > 27000 string_pattern .txt


already seen the string pattern as much as 27000 character, continue with  place the string on a fuzzer,,


run as before..

Now use the pettern_offset application will calculate how many bytes of data from the initial pattern to stirng contained in such registersdo konsole as below :


rebuilds created to change the value of the EIP be DEADBEEF, as follows:

run as before, then the results are as follows :


then run the following steps,
Click the View-> Executable modulesthen it would appear like the following  :


If it looks like the above, proceed to determine which libraries you want to use, double click on the file name, then it will appear as follows.
It appears as below, now do right click in the maiwindow: Search For-> Command.


the input  JMP ESP in window and press the find Command Find


continue by created a mouse button as follows :


run it back like before so that the results are as follows:

then right click Select BreakPoint->Memory, on access


now run by making a payload, do as follows :

Open a web browser, go to the address http://127.0.0.1:5555.
the configuration menu of the payload type of the shell, as shown in the following :

If the visible rows of the opcode of the payload code has been selected, as follows:

now, just enter the payload code into existing application fuzzer that has previous white.


check back payload by using Ollidbg and Easy RM MP3 converter, next run with # telnet 192.168.56.101 4444